A Hacker News post this week, "Show HN: Steal My Bitcoin," does something unusual with a security scare. Instead of arguing about how dangerous a recent PHP remote code execution (RCE) bug is, its creator put Bitcoin on the line and invited anyone to take it. By the end of this article, you'll understand what that experiment is testing and have a simple, repeatable way to judge whether a vulnerability headline actually applies to you.
What happened
The project was posted to Hacker News under the name Stealmybitcoin. The author's description reads: "Made this because I'm curious if anyone out there has figured out how to actually use this PHP RCE we spent the last few days panicking over. Have fun!"
The post had drawn 440 points and 264 comments at the time of capture. I can't tell you from the source material how the challenge is set up, how much Bitcoin is involved, or whether anyone has succeeded. What the post does show is the idea behind it: a live test of whether a scary-sounding bug can be exploited in practice.
What "RCE" means in plain English
Remote code execution means an attacker who is somewhere else on the internet can make your server run commands they chose. That's why RCE bugs set off alarms. In the worst case, the attacker controls the machine.
PHP is a language that runs a huge number of websites, so an RCE-related issue in it gets attention fast. But "a bug exists" and "my site can be taken over" are two different statements. The gap between them is exactly what this challenge pokes at.
Why a bounty-style challenge is useful
Security advisories describe what could happen under certain conditions. A challenge like this asks a harder question: can someone actually do it against a real setup? If nobody can, that suggests (but doesn't prove) the bug is harder to use than the headlines implied. If someone does, the risk just became concrete.
Treat any result with caution. One unbroken target doesn't make a bug harmless, because your configuration may differ from the challenge's.
A five-step check for any vulnerability scare
You don't need to be a developer to run through this. If you manage a website, ask your host or developer these questions.
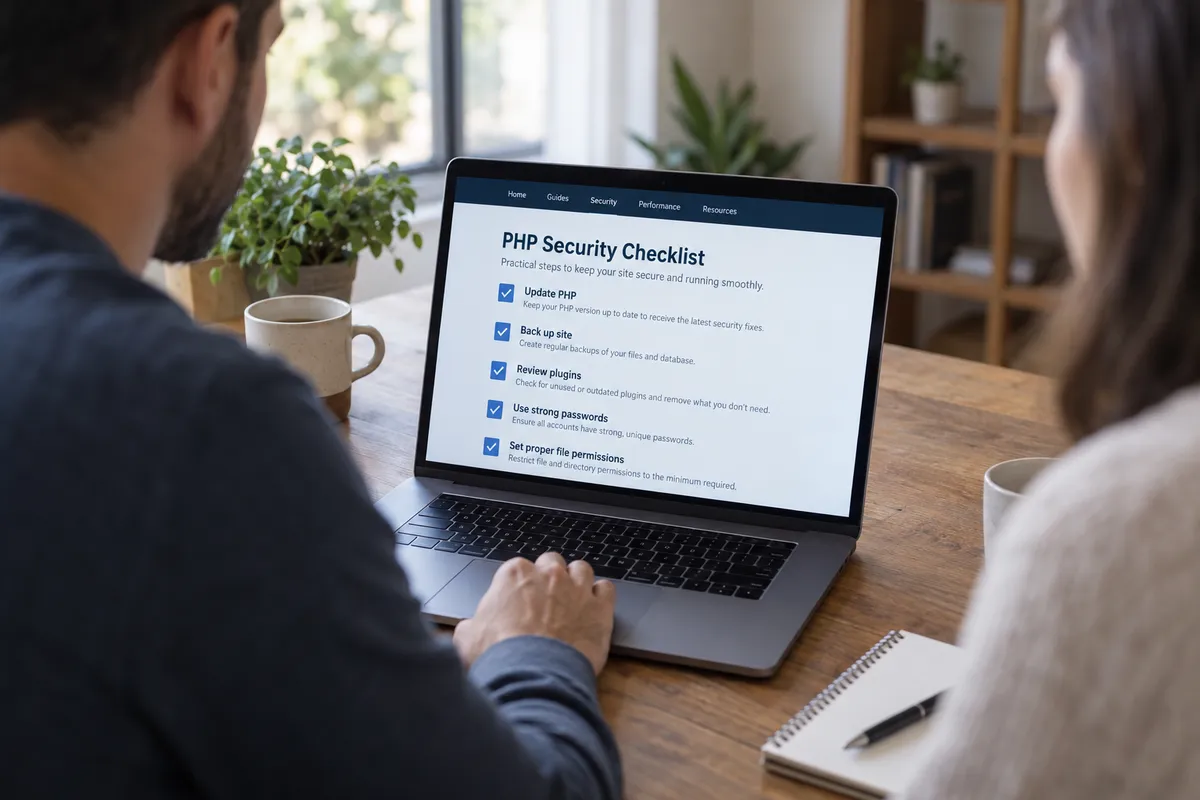
Step 1: Find your PHP version
In a WordPress site, go to Tools, then Site Health, then Info, then Server, and look at the PHP version. Other site builders usually show it in the hosting control panel. Write the exact number down.
Step 2: Read the official advisory
Look for the PHP project's own announcement or your hosting provider's notice. Check which versions are named as affected and whether your number is on the list. Skip the social media summaries for this step.
Step 3: Check the conditions
Many serious bugs only work with a specific setup, such as a certain server configuration or a feature turned on. The advisory should say. If your setup doesn't match, your real risk is lower.
Step 4: Update
If a fixed version exists, apply it. Most hosts let you switch PHP versions from the control panel. Back up your site first, then update, then click through your main pages to confirm nothing broke.
Step 5: Ask your host what they've done
Managed hosts often patch quietly or add protective rules. A short support message asking whether your plan is covered can save days of worry.
Why developers panic, and why you can pace yourself
RCE is the category security teams dread, so the first reaction to any such report is urgent. That's reasonable: it's cheaper to check and find out you're safe than to ignore it and be wrong. But panic isn't a plan. The five steps above turn a vague fear into a short to-do list, and most of it takes under an hour.
A note on ethics
Challenges like this one invite people to attack a target the owner has offered up. That's different from probing other people's sites, which is illegal in many places and harmful regardless of intent. If you want to learn how exploits work, use targets that explicitly invite testing, or set up your own practice environment on a computer you own.
The takeaway
Next time a vulnerability dominates your feed, don't ask how scary it sounds. Look up your PHP version, read the official advisory, and update if you're affected.